On-premises Exchange Server configuration
Introduction
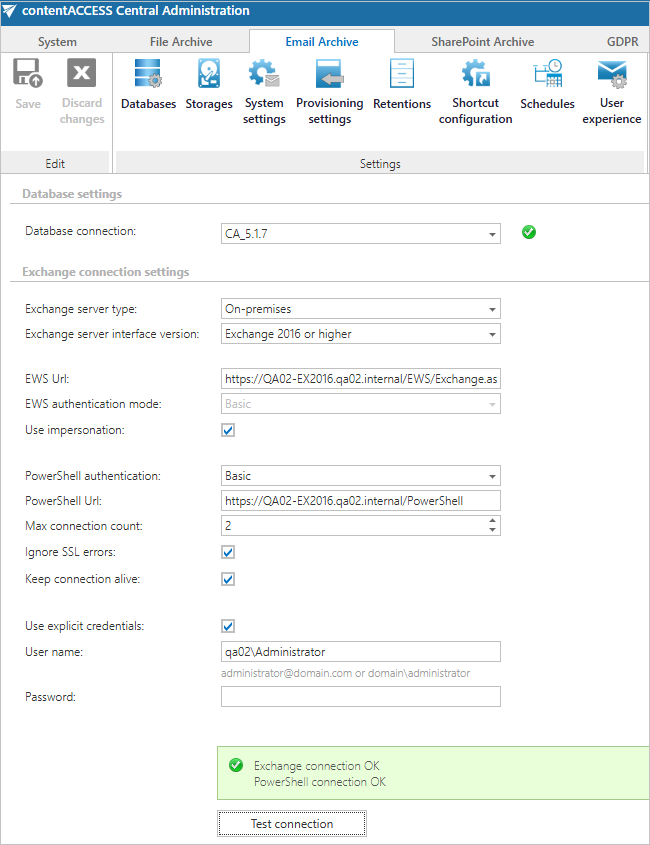
The On-premises Exchange Server configuration page allows administrators to configure the connection between contentACCESS Email Archive and an on-premises Exchange Server. These settings are available under Email Archive => Settings => System settings on the ribbon.
From this page, you can:
- Configure the Exchange connection type and interface version.
- Set up EWS (Exchange Web Services) and PowerShell access.
- Configure the credentials used by contentACCESS to connect to Exchange.
- Test the connection to verify that it is working correctly.
- Review the superuser permissions and access methods (impersonation or delegation) required for on-premises Exchange integration.
Note: Before you begin the configuration, select or create a user account with a valid mailbox license. This account is used as the superuser to access mailboxes. The permissions required for this account are described later on this page.
Exchange connection settings
Set the Exchange server type to "On-premises".
Select the Exchange server interface version corresponding to your Exchange Server version. Since older Exchange Servers have already reached end-of-life, the recommended version is Exchange 2016 or higher.

EWS connection settings
Access to an on-premises Exchange Server always uses EWS (Exchange Web Services) with Basic authentication.
- EWS URL: The URL used to connect to Exchange Web Services, in the format
https://servername/EWS/Exchange.asmx. - EWS authentication mode: Fixed to "Basic" authentication.
- Use impersonation: Determines how permissions on mailboxes are managed in your organization:
- Delegation (without impersonation) requires explicitly granting Full access permissions on all archived mailboxes.
- Impersonation requires an account with the ApplicationImpersonation role.
It is recommended to use impersonation. For more details, see Microsoft 365 superuser mailbox configuration.

PowerShell connection settings
Configure the following options to enable PowerShell access:
- PowerShell authentication: It is recommended to use the same Basic authentication as used for EWS. Note that Basic authentication for PowerShell might not be enabled by default and needs to be enabled on the Exchange Server (by configuring the PowerShell virtual directory).
- PowerShell URL: The URL used to connect to PowerShell, in the format
https://servername/PowerShell. - Max connection count: Limits the number of concurrent connections made by contentACCESS to PowerShell. The recommended value is
3. - Ignore SSL errors: Use this option only if the Exchange Server has a self-signed certificate. If the certificate is valid, this option can be left unchecked. Test the connection to determine whether certificate errors occur.
- Keep connection alive: Allows contentACCESS to reuse existing connections instead of creating a new one when needed. While this can improve performance, it might cause issues, especially when a load balancer is used. It is recommended to turn off Keep connection alive when using a load-balanced Exchange Server.

Credentials
Both the EWS connection and the PowerShell connection use the same account, configured under Username and Password. It is recommended to use Use explicit credentials to specify this account.
If an explicit account is not selected, contentACCESS must be configured to run under a specific Active Directory account. For more information, see the Installation section and Microsoft 365 superuser mailbox configuration.
When entering the explicit account, you can use either the DOMAIN\user format or the UPN format user@domain. Use the format accepted by your Exchange Server.

Test the connection
It is recommended to test the connection after each change. Both the EWS and PowerShell connections are tested, and the result is displayed.
Portal access
contentACCESS can provide access to archived data for users through Portal access user logins, configured on the Email Archive provisioning settings page.
When working with an on-premises Exchange Server, it is recommended to configure the Active Directory connection in System settings. Users can then use Windows authentication to log in to contentACCESS. Email Archive creates the Windows logins for the users and synchronizes permissions based on these Windows logins.
Superuser permissions
The superuser account must be an active account with a valid mailbox license. The account requires the following Exchange roles:
- ApplicationImpersonation (for impersonation)
- View-Only Organization Management or Organization Management
- Org Custom Apps
- Org Marketplace Apps
- User Options
The roles Org Custom Apps, Org Marketplace Apps, and User Options are required for the installation and usage of contentACCESS MailApp.
The following superuser access methods are available:
- Impersonation (recommended)
- Delegation
Impersonation
Impersonation allows the superuser to impersonate any account in the organization and access mailbox data. Configuring impersonation is simple: grant the ApplicationImpersonation Exchange management role to the account.
Benefits:
- The impersonating account has access to all mailboxes in the organization.
- New users are automatically granted permission; no further action is needed.
- Throttling is less likely to occur.
Drawbacks:
- To restrict permissions to certain users, an additional management scope needs to be created.
Note: The following script creates a dedicated role assignment in Exchange and grants the ApplicationImpersonation role to the superuser:
New-ManagementRoleAssignment -name:contentACCESSImpersonation -Role:ApplicationImpersonation -User:superuser
For more details about impersonation, see How to configure impersonation.
Delegation
To access accounts in the organization, the superuser must be granted as a delegate user on each account individually. The superuser is granted Full mailbox access on all accounts. This can be done either at the mailbox database level (for all Exchange mailbox databases) or at the user level using the Exchange Management Shell.
Configuring delegation is more complicated and requires the administrator to set permissions on newly created mailboxes regularly.
Benefits:
- Useful if only certain users are archived.
Drawbacks:
- Complicated configuration; ongoing maintenance needed.
For more information about connecting to Exchange PowerShell and configuring the required superuser permissions (including delegation and impersonation), see PowerShell scripts for setting up Email archive.