Teams archive Address book
Introduction
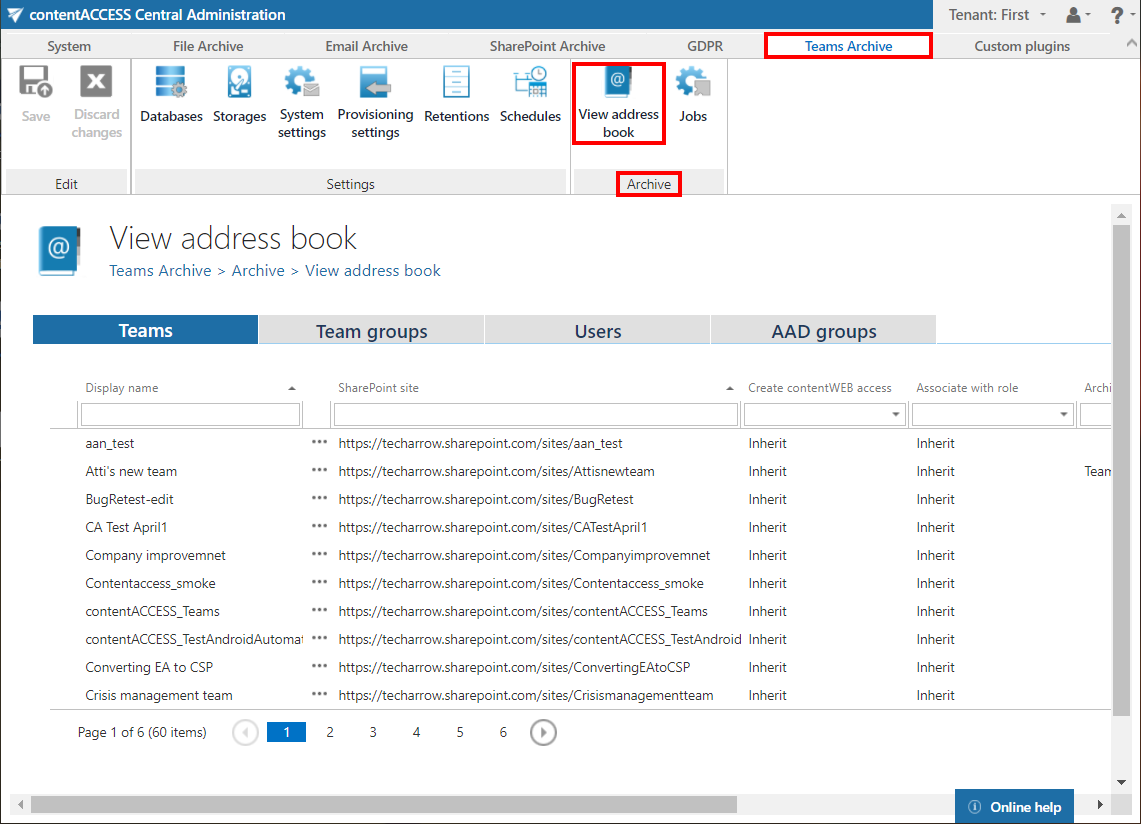
The View address book page in Teams archive provides a read-only list of objects provisioned in the address book, including Teams, Team groups, Users, and AAD groups. From this page, administrators can review object details, manage team groups, assign archiving settings such as database, storage, and index zone, and control contentACCESS Portal access and object status.
To open the page, navigate to Teams Archive ⇒ Archive ⇒ View Address Book:
Team groups
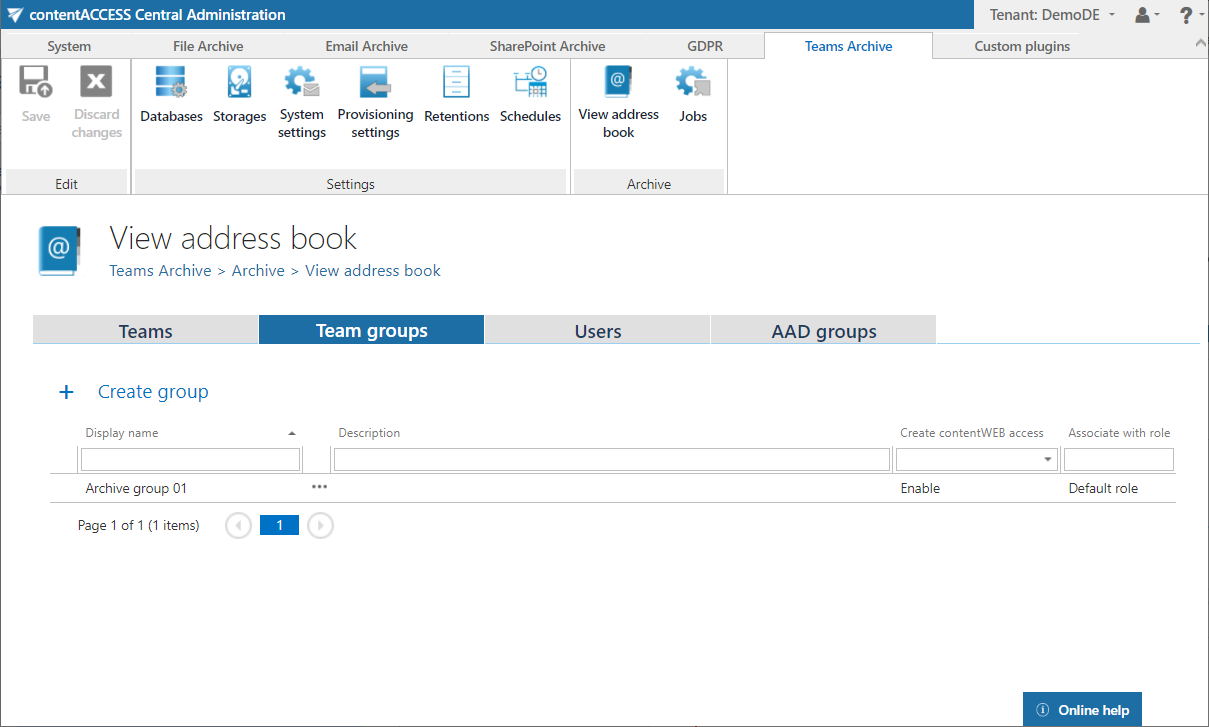
To simplify management of the address book, contentACCESS provides the option to group teams into Team groups. This is especially useful, and recommended, when the same archiving policies need to be applied to multiple teams (same database, store, index zone, contentACCESS user creation policy, etc.).
Objects can be added to the address book in the following ways:
- By the provisioning job (Teams, users, AAD groups).
- Created manually from the address book (Team groups).
A team group can be created in two ways.
From the Team groups tab:
- Click + Create group. A pop-up window opens.
- Enter a name and, optionally, a description for the group.
- Click Create.
The new group is added to the list of groups in the Team groups tab.
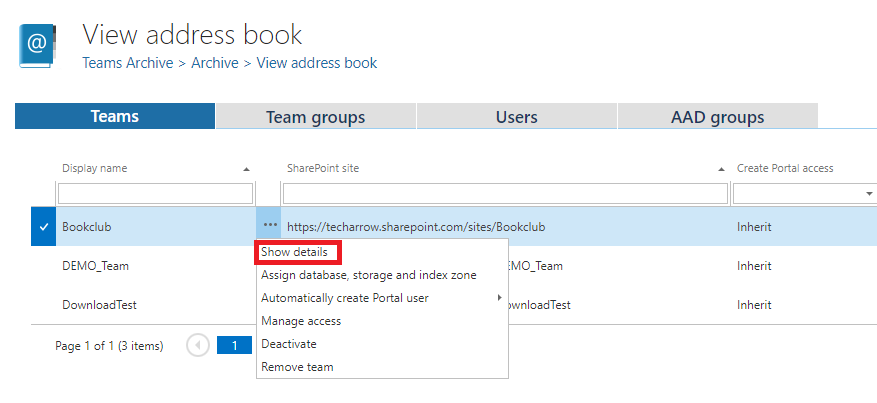
From the Teams tab:
- Select the desired team and click Show details in its context menu.
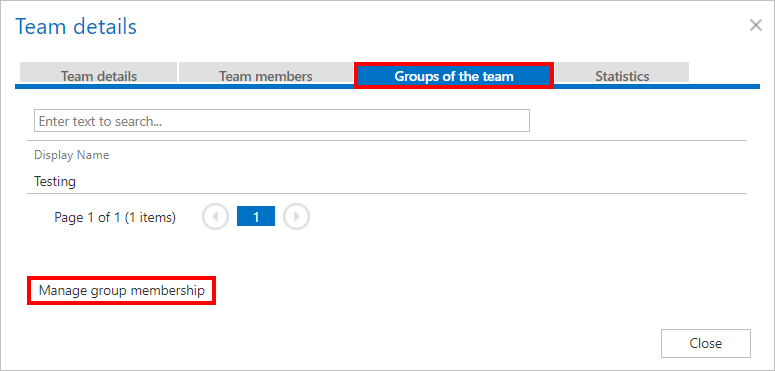
- Switch to the Groups of the team tab and click Manage group membership.
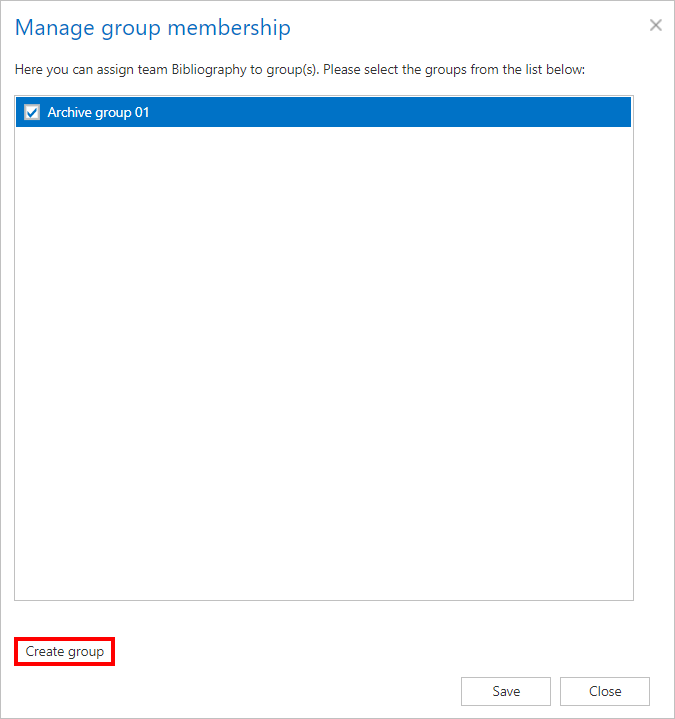
- Click Create group, or assign the team to one of the previously created groups.
Address book tabs and columns
The address book objects are organized into four tabs: Teams, Team groups, Users, and AAD groups.
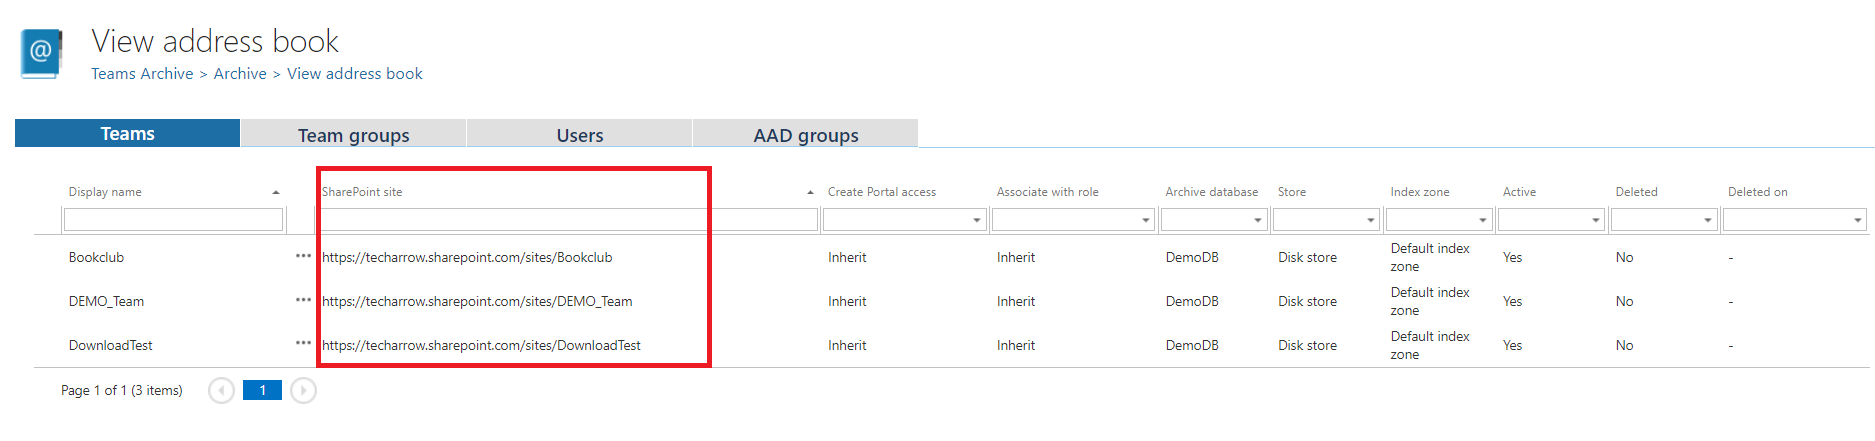
- SharePoint site: Displays the SharePoint site where the content of the Team is stored.
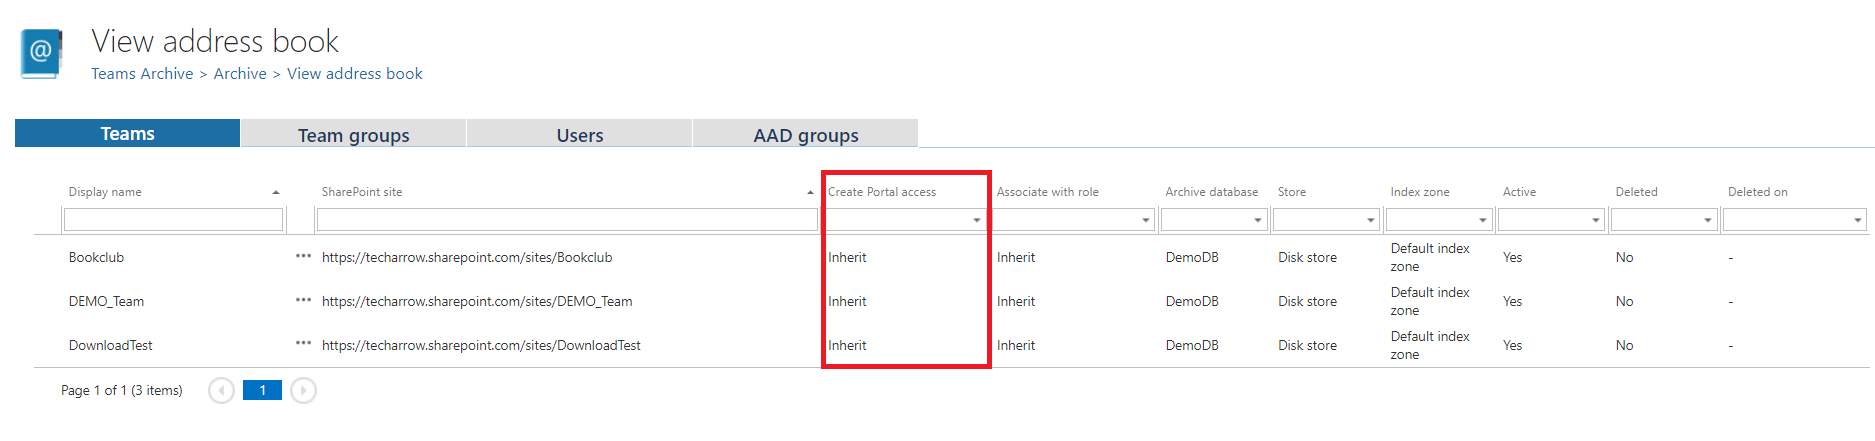
- Create contentACCESS Portal access: Indicates whether there is a command for the provisioning job to create contentACCESS Portal users for the selected object.
- On the Users tab, an Inherit value means that the teams of the user and the groups of those teams will be checked.
- On the Teams tab, an Inherit value means that the value set for the group of the team will be used. If the team belongs to more than one group, the user will be created if at least one of the groups has contentACCESS Portal user creation enabled.
- Once contentACCESS Portal access is granted (the provisioning job must be run), every user of the provisioned object will be able to access the archived content of the objects for which they have the necessary permissions.
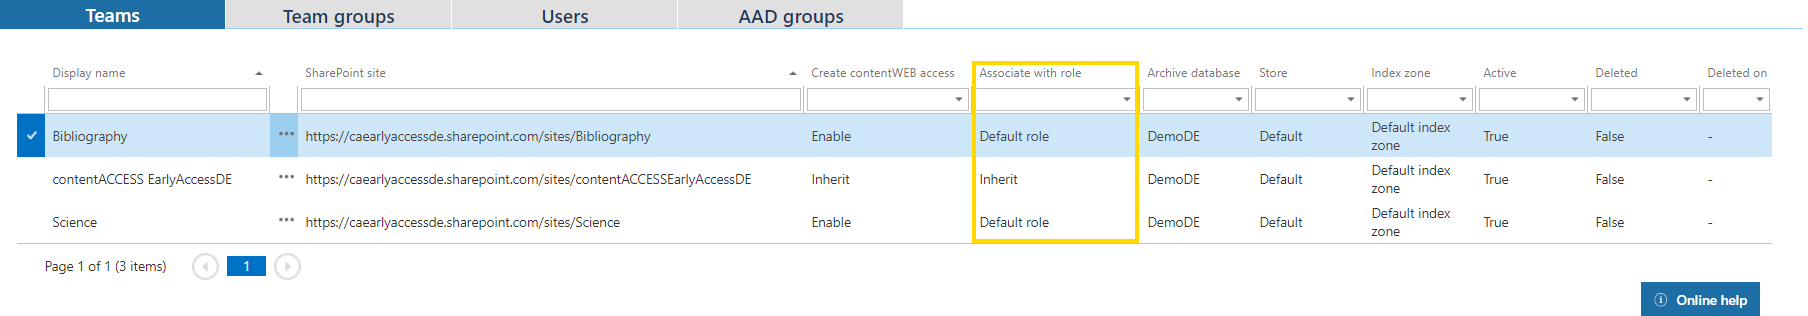
- Associate with role: Displays the role assigned, or to be assigned, to the object by the next running Teams provisioning job. By default, objects inherit the default role specified in the Teams archive provisioning settings, but the administrator can assign custom roles to individual objects.
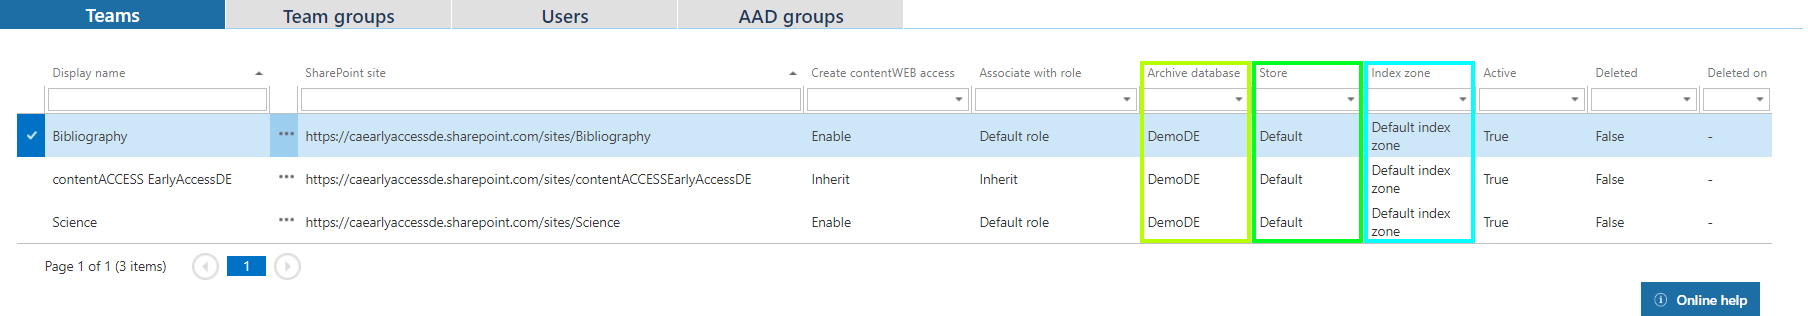
- Archive database, Store, and Index zone: Display the Teams archive database, storage, and index zone assigned to the objects. Database and storage are assigned automatically by the first running archive job, or manually using the object's context menu (used when the selected team to be archived does not yet have an associated database and storage). If a team does not have an index zone assigned, the next running indexing job will assign the index zone set in its configuration.
-
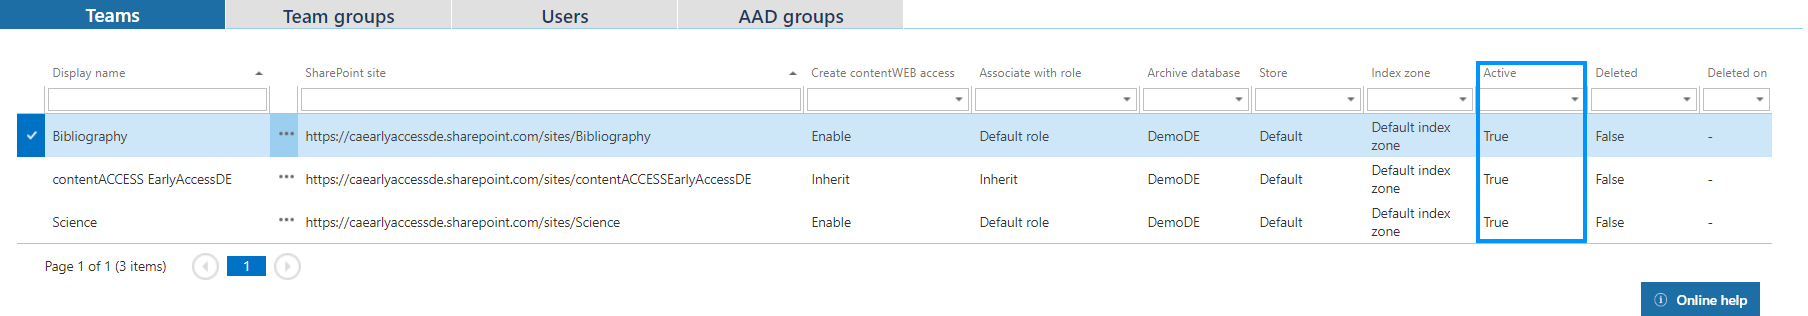
Active: Shows whether the respective object is active in contentACCESS. This feature allows administrators to deactivate no longer used objects, keeping the licenses under control. Deactivated objects are not touched by the Teams archive job, nor are they counted toward the licensed objects.
infoNote: To set an object to active or inactive, the telemetry job must also be run. It runs automatically every day, or can be started manually on the Licensing page (System tab ⇒ Services group ⇒ Licensing, option Update telemetry).
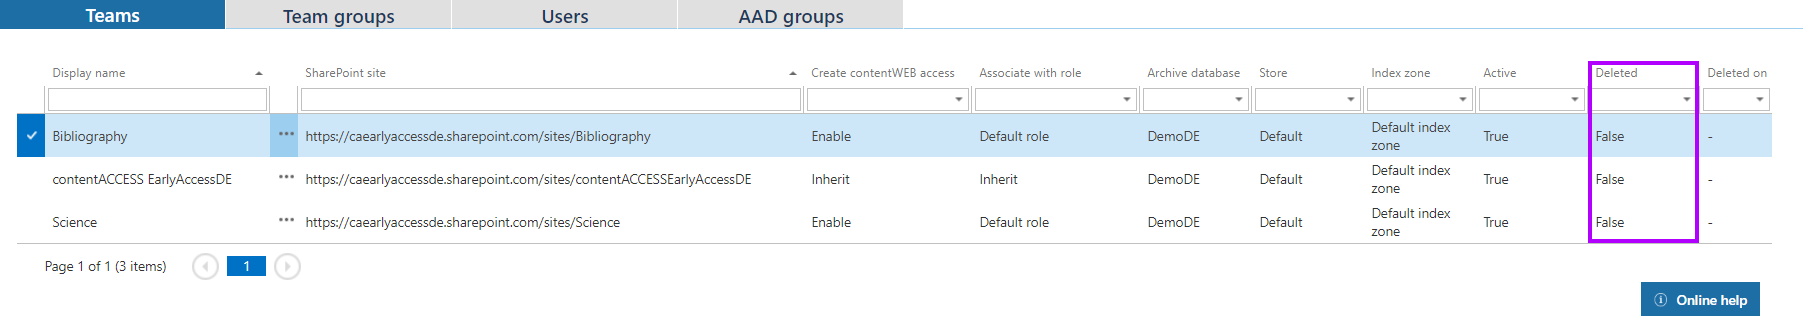
- Deleted: Shows whether the selected team was deleted from Teams.
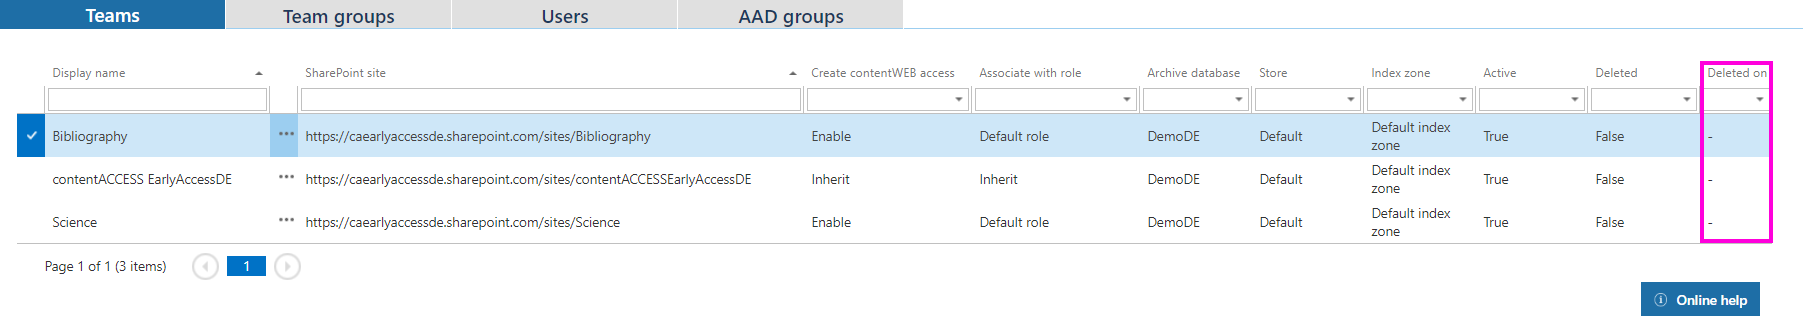
- Deleted on: If the selected team was deleted, shows when it was deleted.
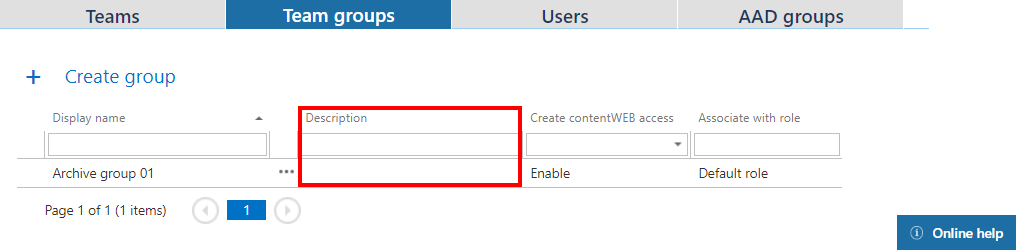
- Description: Shows the description written for the selected group.
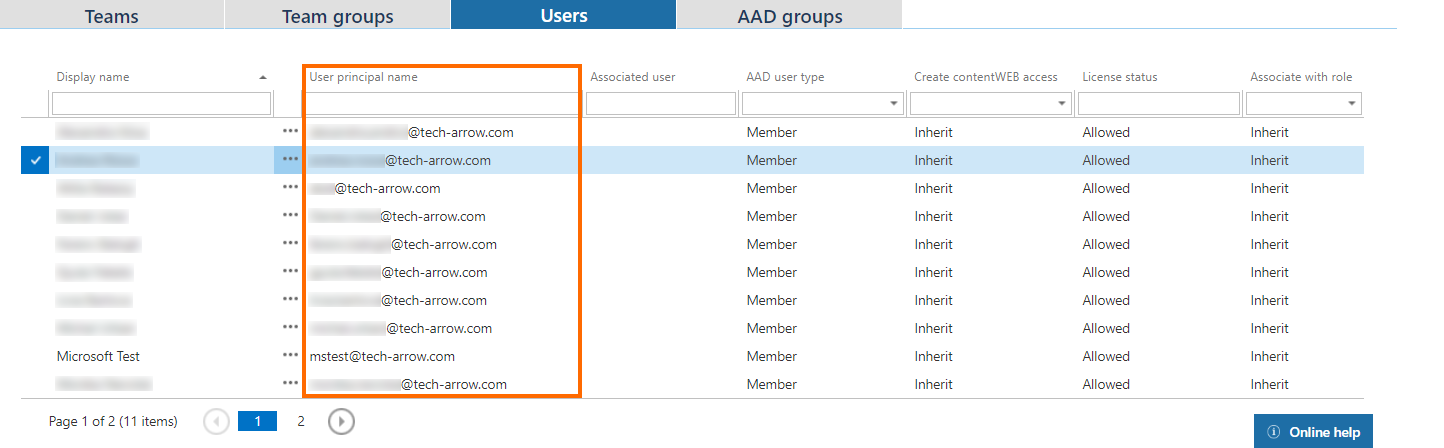
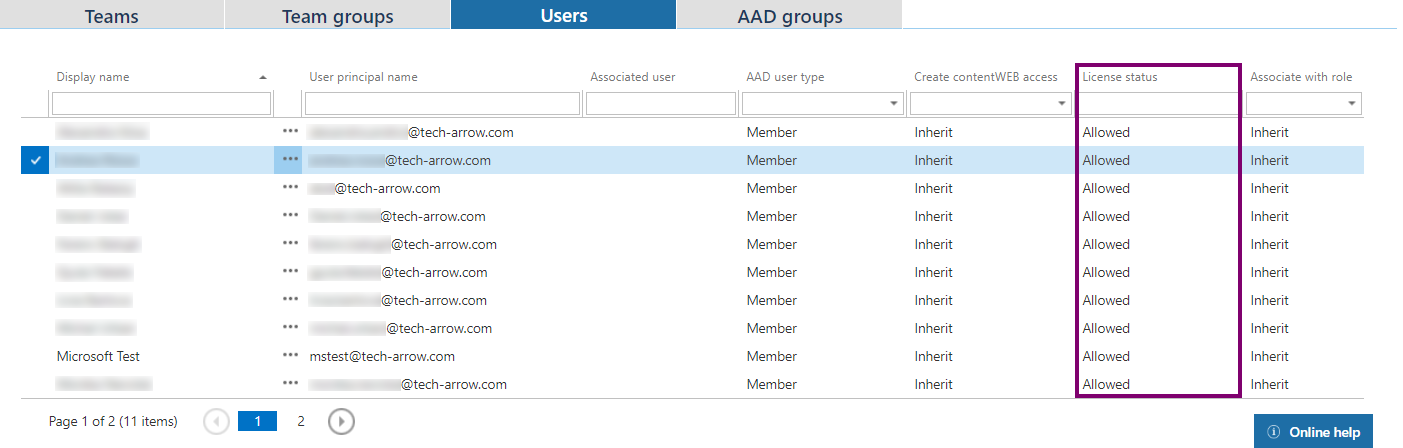
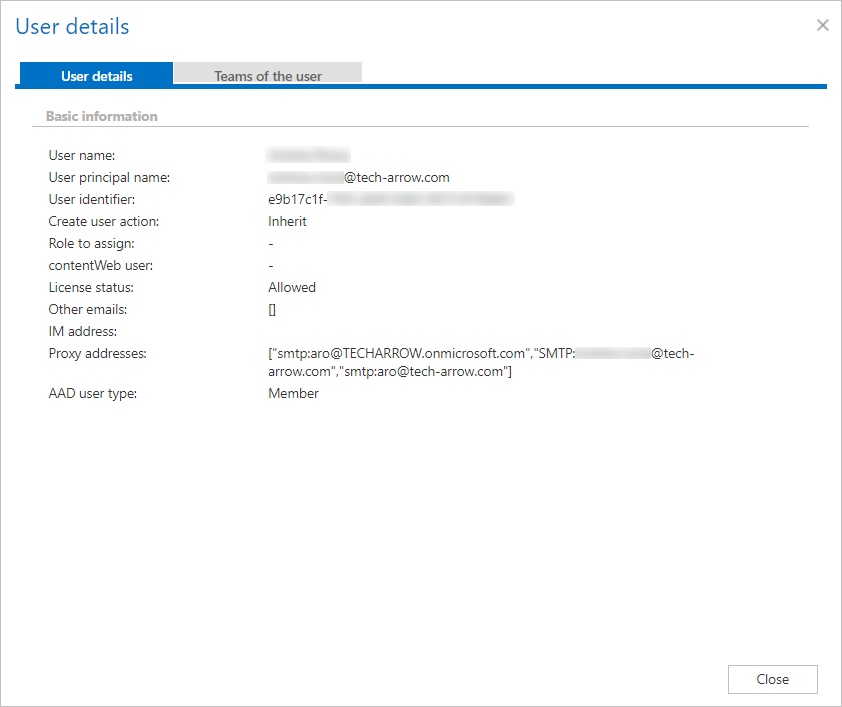
- User principal name: Displays the email address that the user uses to log into Teams.
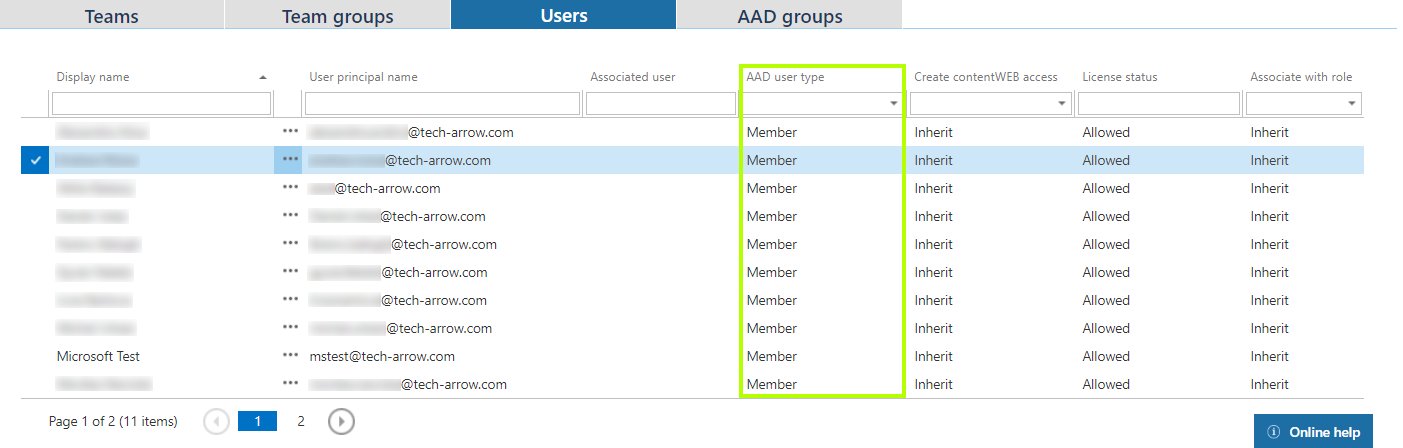
- AAD user type: Shows the user type of the selected user in Azure Active Directory. There are two options: Member and Guest.
- License status: Shows whether a license is assigned to the user, and therefore whether the user can be archived.
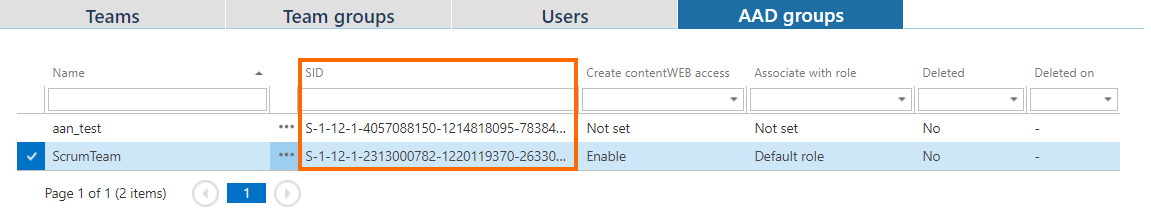
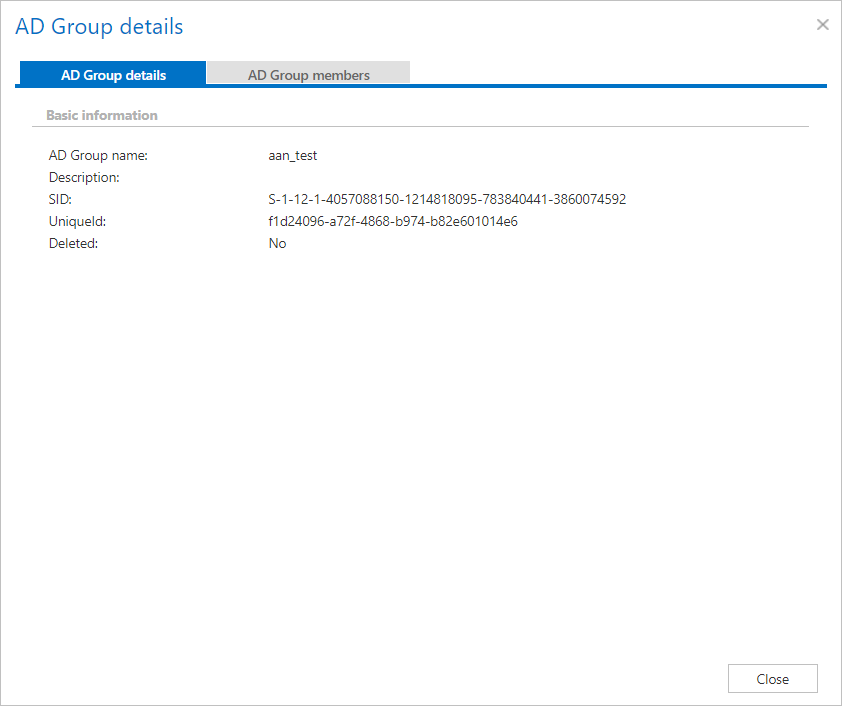
- SID: Shows the security identifier of an AAD group.
Context menu actions
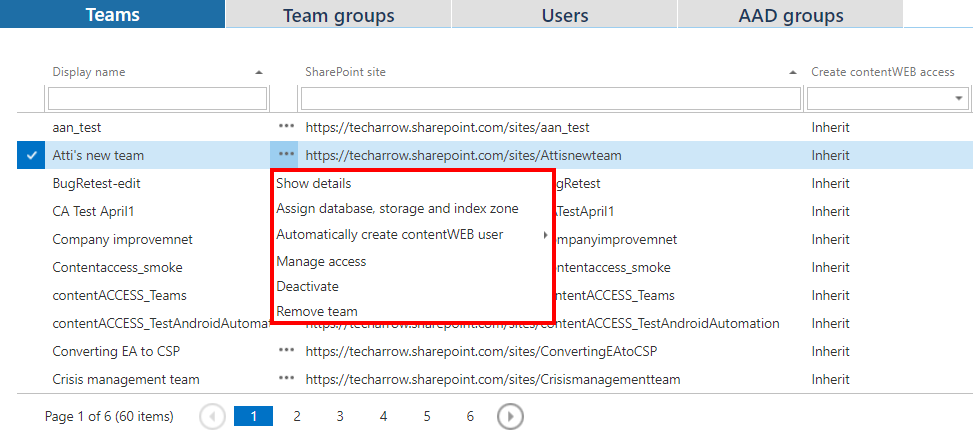
Using the context menu of a team, group, or user, an administrator with the necessary permissions can:
- View object details.
- Assign database, storage, and index zone for Exchange groups and mailboxes.
- Automatically create a contentACCESS Portal user, including with custom permissions.
- Manage access for additional users to the selected Teams and Users.
- Activate or deactivate objects. Users can be deactivated only directly from the Users tab; otherwise, only teams are deactivated.
- Remove a team, group, user, or AAD group.
Object details
Clicking Show details opens a pop-up window showing detailed information about the selected object, organized by object type.
Teams
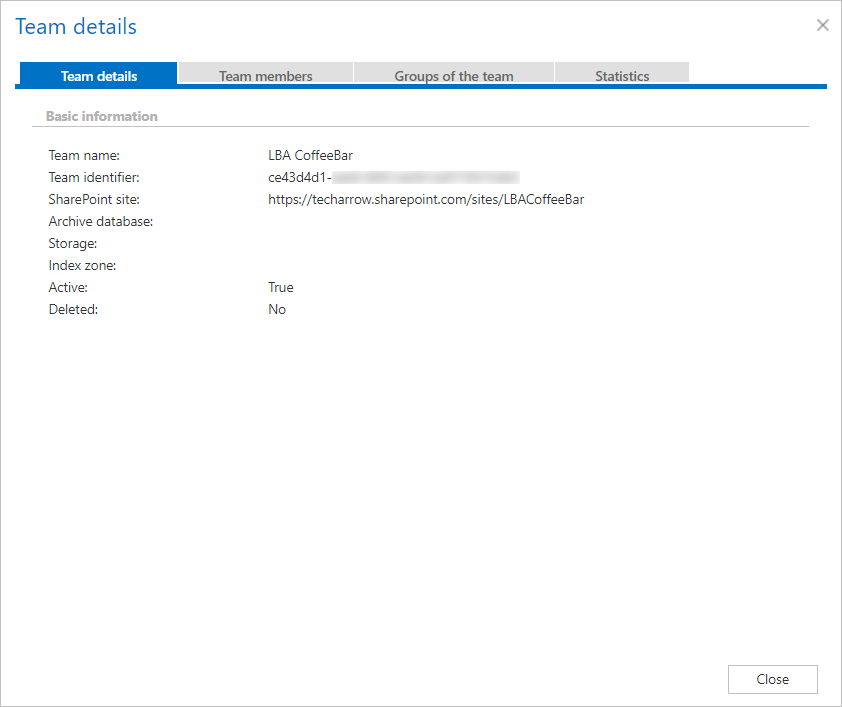
- Team details: Displays basic information about a team, such as name, storage, index zone, etc.
- Team members: Displays the members belonging to the currently selected team.
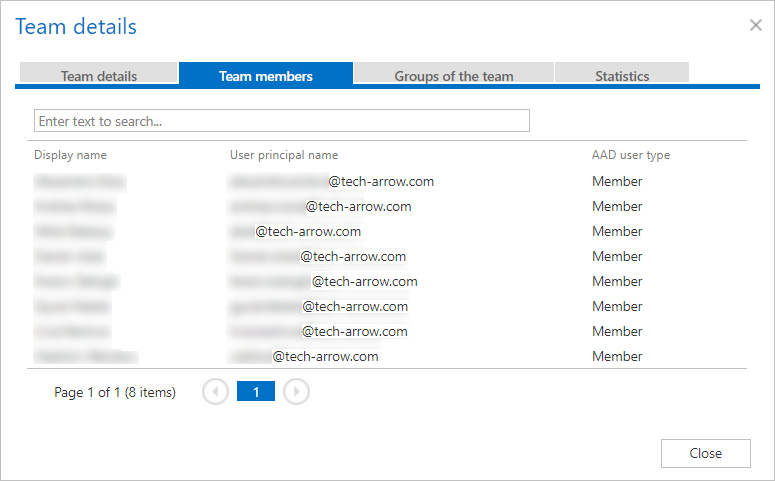
- Groups of the team: Allows you to manage group membership and create new groups, as described above in this section.
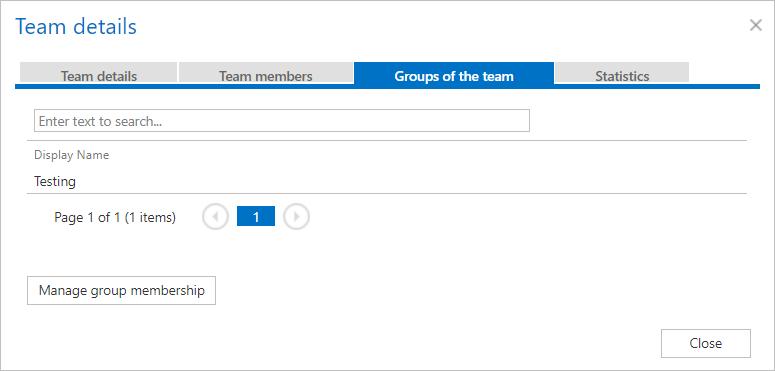
- Statistics: Displays the archive statistics and index statistics of the currently selected team.
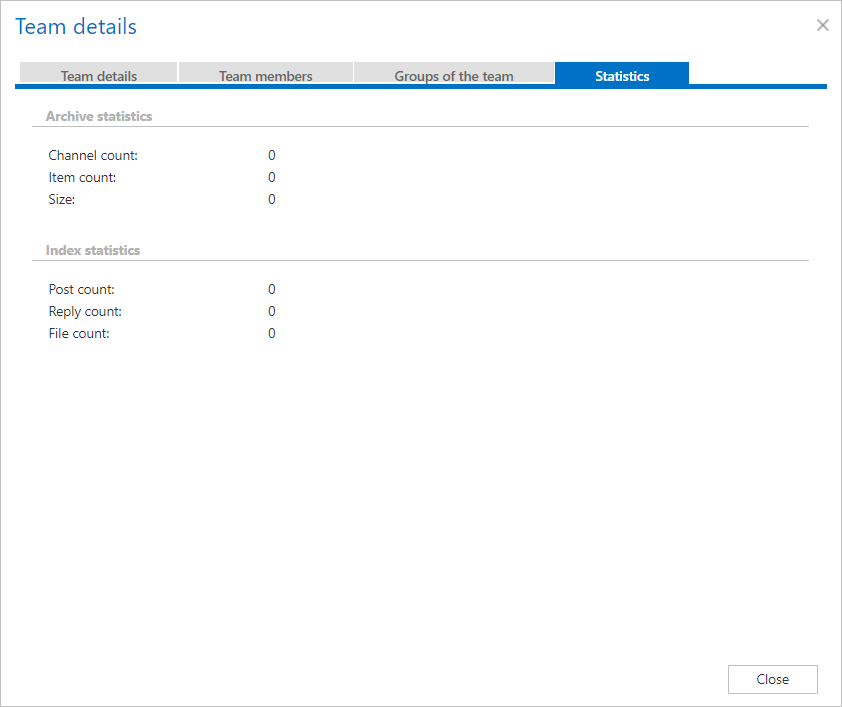
Team groups
- Group details: Displays the name and description of the currently selected group.
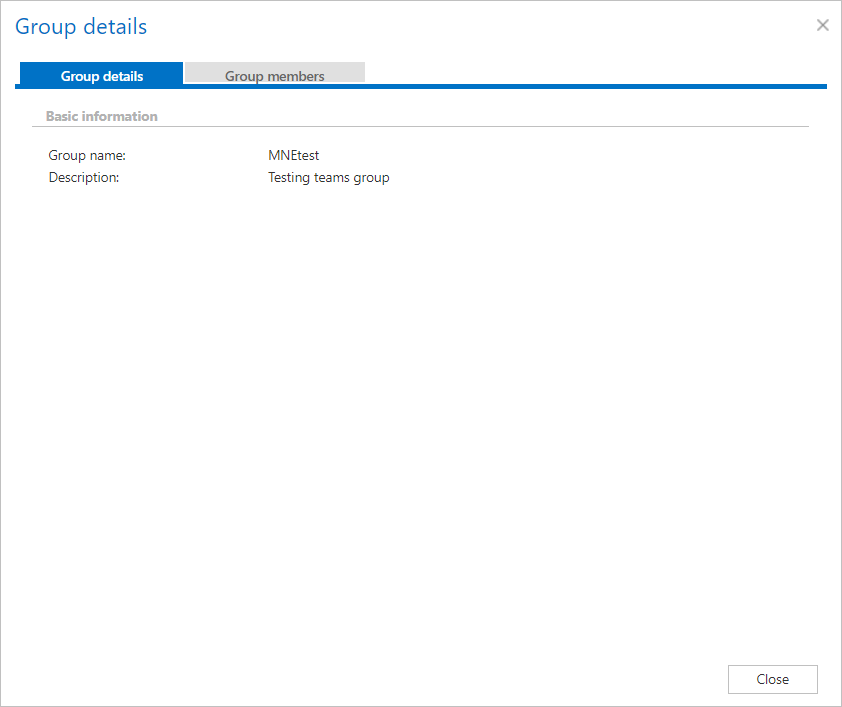
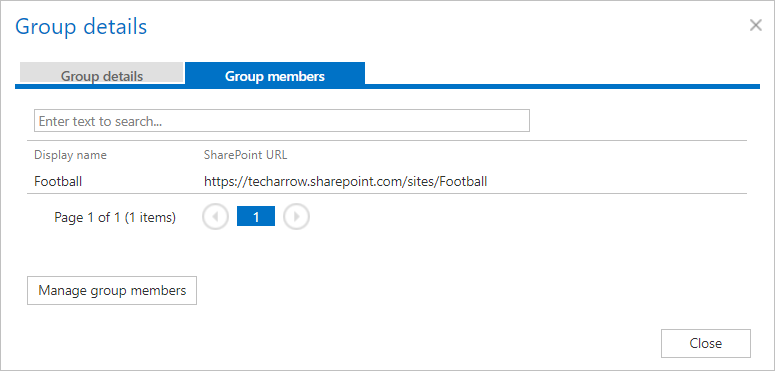
- Group members: Displays the members of the currently selected group and their SharePoint URL. From here, you can also create a new group by clicking Manage group membership.
Users
- User details: Displays basic information about a user, such as name, principal name, license status, AAD user type, etc.
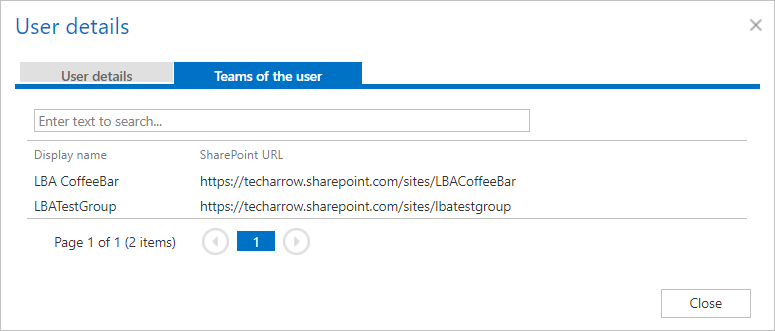
- Teams of the user: Displays a list of the teams the currently selected user is a member of, along with their SharePoint URL.
AAD groups
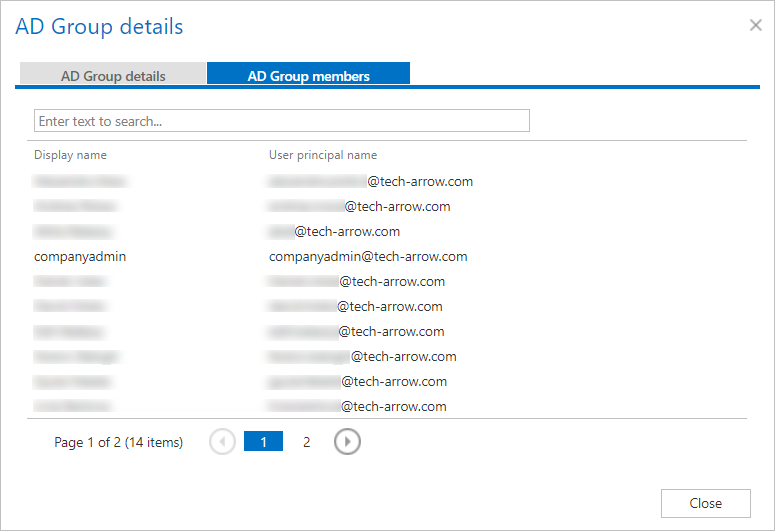
- AD Group details: Displays basic information about an AD group, including name, description, SID, UniqueId, and whether the group is deleted.
- AD Group members: Displays all members of the selected AD group.